Picture a guy in a hoodie, sitting at a computer with several screens. They’re full of green letters on a black background, and maybe a few progress bars showing a percentage. This is the classic film hacker, a computer genius. It doesn’t matter whether his target is an enemy spy or the government; with his experience and the right sequence of keys, sooner or later he’ll get into his opponent’s computer and do some damage. But how true is that? Will there really always be a point where someone can hack something?
Think of a wooden door on a house. We know it keeps most people out; still, someone could pick the lock or, perhaps, someone more desperate could take an axe or a battering ram to it and force their way in. Swap it for a metal door and you might get through with a blowtorch, an angle grinder or some explosives. Every time you make the door more secure, you could find a more powerful method of attack to beat it. Does that really happen with cybersecurity? However far algorithms advance, will there always be some way to beat them?
In the digital world, we can’t make harder bits, or programs that need harder keystrokes to break; what we have to protect ourselves is maths, problems so difficult that not even today’s most powerful computers could solve them.
Throughout history, algorithms have kept changing. The first computers were so slow that they couldn’t cope with legitimate use unless they ran a lightweight algorithm, and over time those algorithms were broken. Some simply because computers became powerful enough to break them quickly; others because vulnerabilities were found in them, mathematical shortcuts that let you skip the algorithm.
Today, however, we have algorithms that, as far as we know, neither current computers nor future ones could break, quantum computers included. We’ve reached a point where the maths is so solid that an attacker is better off looking for a way around the algorithms than for a way to break them. We have algorithms that are practically impossible to break, to the point that the biggest weakness is human error, like leaving the door unlocked or even leaving a hole where a door should be.
When I was in high school, during the golden age of the cyber[1], a lot of people had their accounts hacked. Many thought it was an inherent weakness of the internet: with enough knowledge and resources, there had to be a way to steal any account.
I knew there were three possible explanations:
-
They’d clicked “remember my password” on the cyber’s computer. The next person who used it got straight in.
-
Their password was so easy that someone they knew guessed it. They’d used their birthday or their dog’s name.
-
That computer had a keylogger: an application that recorded every key pressed. This happened more often than you might expect.
The first was the most likely. But in all three cases, the weak point was the person or the computer they used. The server didn’t even notice. And in a properly built service, even if someone had got into the server, the password shouldn’t have been there in the first place.
One-way algorithms
When you create an account on a properly built website, the site doesn’t save your password. It saves a number calculated from it using a hash function.
Let’s invent a very simple one. Give each letter its position in the alphabet: a = 1, b = 2, c = 3, all the way to z = 26. The hash of a word is the sum of its letters. We’ll keep the Spanish words for these examples so the sums stay the same.
hola → 8 + 15 + 12 + 1 = 36
Change one letter to make hora and you get 42. A different number, with no obvious pattern at first glance. There is one, though.
Here’s the important part. If I tell you “the number is 36”, can you tell me what the word was? Mathematically, no. The sum loses information: you no longer know which letters were there or what order they were in.
These one-way algorithms are called “hash functions”. Servers use them to store passwords, or at least they should. If someone steals the database, they’ll see 36, but they won’t know your password. They’d have to try words until one produces 36.
With our simple function, that’s very easy. Try common words like hola and vida: both give 36, so either one could get you into the account. When two different inputs produce the same result, it’s called a collision. This algorithm has loads of them: amor, roma, ramo, mora and pez all give 47. If your password is amor, someone could log in with pez, because both produce the same result.
To avoid that, services use algorithms such as SHA-256. The idea is similar, but they’re much more complex. Instead of adding letters, SHA-256 mixes the input’s bits through 64 rounds of operations and produces a 256-bit number. Here’s the hash of hola:
b221d9dbb083a7f33428d7c2a3c3198ae925614d70210e28716ccaa7cd4ddb79
And here’s Hola, with a capital H:
e633f4fc79badea1dc5db970cf397c8248bac47cc3acf9915ba60b5d76b0e88f
Change one letter and you get a completely different result, with no visible pattern. SHA-256 collisions exist in theory: there are infinitely many possible words but only finitely many possible results. Nobody has found one, though. There’s also no known way to take a hash and manufacture a word that produces it. These days, password storage uses even more complex algorithms, such as Argon2 and bcrypt. They’re deliberately slower to calculate and add random components, making brute-force guessing harder.
So how does the site know you typed your password correctly if it hasn’t saved it? It hashes what you typed and compares the result with the one it stored. If they match, it’s you.
The site itself doesn’t keep your password. If an employee opens the database, they see numbers. If someone steals it, same thing. If the company’s director, or a government carrying a court order, demands your password, they have no way to hand it over. It isn’t that they refuse. It doesn’t exist anywhere, only the hash does. A properly built service never tells you what your old password was. If you forget it, you’ll have to create a new one, because even they don’t know the previous one.
Unfortunately, not every service does this. Once I used Telcel’s password-recovery process. Telcel is a mobile operator in Mexico. They sent me my actual password, in plain text. The scariest part? It was only a few years ago.
Trying different combinations until you get one right still works, though. If your password is too simple, an attacker might guess it very quickly. That’s why password length matters so much. We’ll talk about that in another post.
Access and encryption
Making your password impossible to retrieve is a big protection, but a password is only a check. A coding mistake could bypass it. That’s where encryption comes in.
Encrypting means turning a message into something unreadable that can only be decoded with a key. Unlike a hash, you can get the original message back, but only if you have that key.
Let’s try another simple algorithm, one as old as Julius Caesar. The key is a number, and encrypting means shifting every letter that many places along the alphabet. With a key of 3, hola becomes krod: h becomes k, o becomes r, l becomes o and a becomes d. To get back, shift the letters backwards by the same 3 places. Without the key, krod doesn’t tell you much.
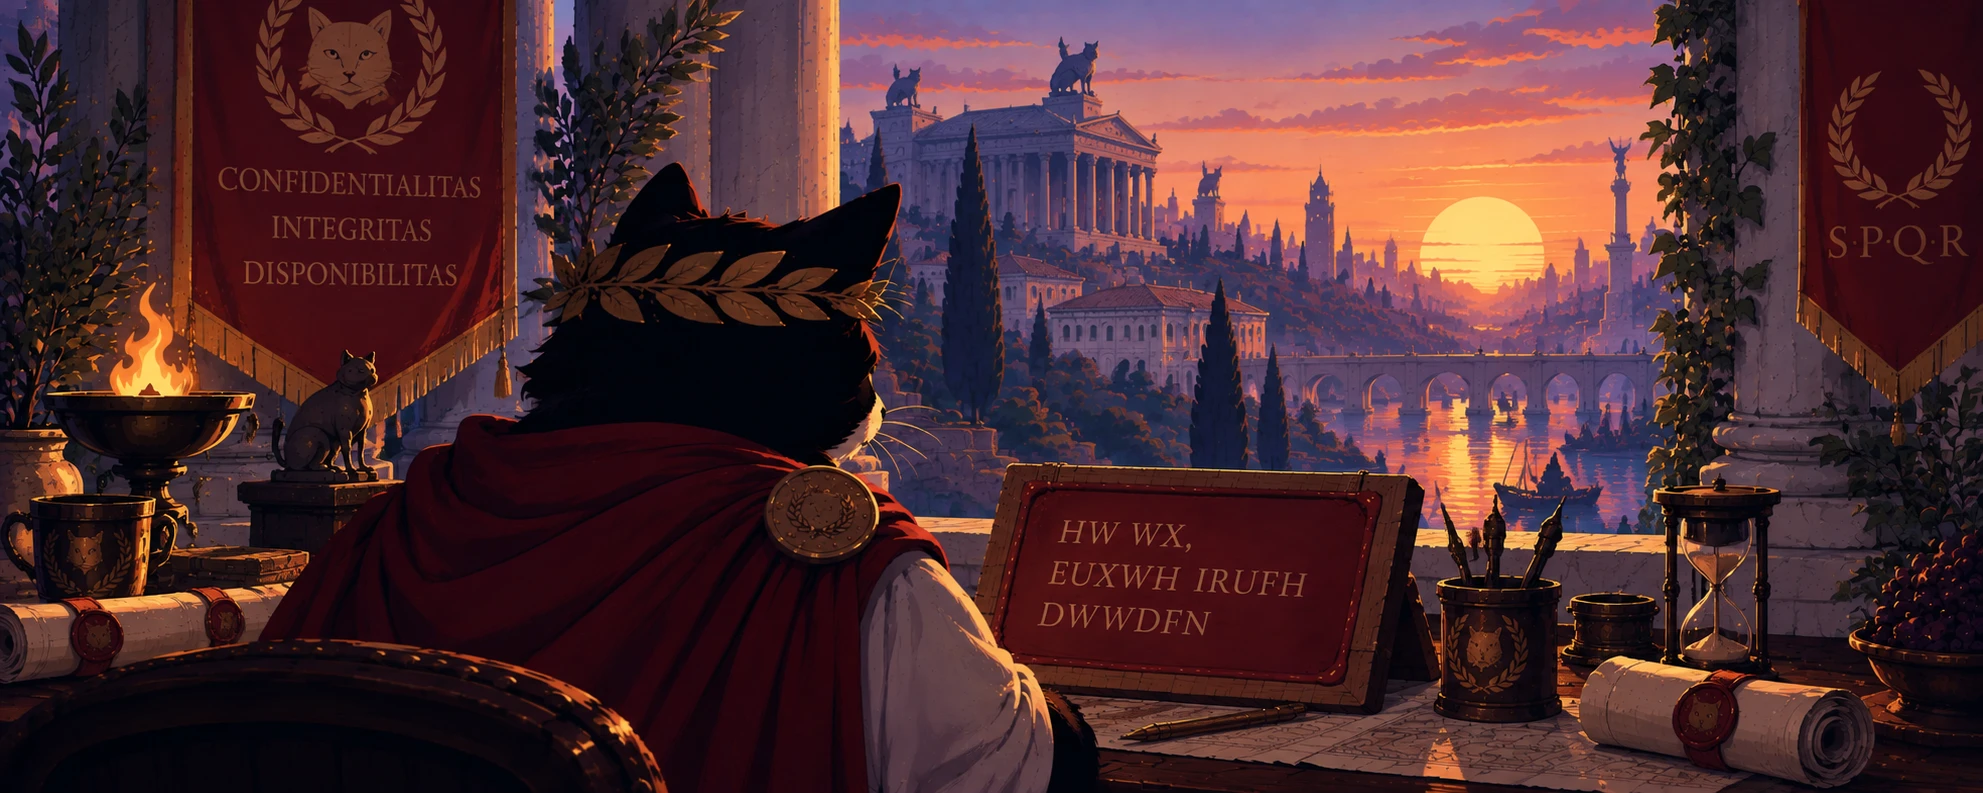
Is it secure? Not at all. There are only 25 possible keys. Someone who sees krod without knowing the key can try them all. Only one produces something readable: a key of 1 gives jqnc, 2 gives ipmb, and 3 gives hola. Sooner or later, trial and error would give them the key.
Let’s make it more complicated. Instead of one number for the whole word, use a different one for each letter: say 7, 2, 19 and 11. Now hola becomes oqel. The attacker has to try 26^4 keys instead of 25, nearly 457,000 combinations. Much safer than before. Still, a recognisable pattern can make the key easier to work out. A computer can solve this very quickly.
Secure ciphers increase the algorithm’s complexity until guessing the key by trial and error becomes very difficult. AES doesn’t shift letters. It works on 128-bit blocks, mixing them through 14 rounds of operations with a 256-bit key. It’s complex enough that there isn’t an easy pattern to exploit; all you can do is try key after key. It’s what protects your messages, your photos in the cloud and your connection to the bank. So even if someone gets into an account through the wrong door, if the data is properly encrypted and they don’t have the key, all they’ll find is noise.
How many keys are there? Our first toy had 25. The second had 26^4. With AES-256, a key can take 2^256 different values. Written out, that’s a 78-digit number.
Imagine a computer that can try a million million million keys a second: a 1 followed by 18 zeroes. That’s already more than any current supercomputer could manage. Trying all of them would take about 3.7 × 10^51 years. The universe is about 13.8 billion years old, so you’d have to wait its entire age more than 10^41 times.
With today’s technology, nobody can break AES-256 encryption, even using every computer on the planet. If a film shows a hacker breaking an enemy spy’s advanced encryption after a few minutes of typing, you now know it’s about as realistic as someone opening a padlock by pointing a wand at it and saying “Alohomora”.
The future isn’t completely settled, though. Quantum computers could solve certain very specific problems faster. For some current algorithms, their mathematical complexity becomes trivial.
As far as is publicly known, quantum computers aren’t yet big enough for that. But there’s already a response for when they are. In 2024, NIST published the first cryptography standards designed to resist quantum computers. Some browsers and messaging apps already use them. They still need to reach everything, but we’re not sitting around waiting. We’ll look at how a quantum computer works, and how we protect ourselves from it, in another post.
In the next post, we’ll tackle something you can control: your passwords, and why a long phrase protects you better than a complicated password like P@ssw0rd!.
References
- NIST. FIPS 180-4: Secure Hash Standard (SHS). https://csrc.nist.gov/pubs/fips/180-4/upd1/final
- NIST. FIPS 197: Advanced Encryption Standard (AES). https://csrc.nist.gov/pubs/fips/197/final
- Biryukov, Dinu, Khovratovich and Josefsson. RFC 9106: Argon2 Memory-Hard Function for Password Hashing and Proof-of-Work Applications (2021). https://www.rfc-editor.org/info/rfc9106
- Provos and Mazières. “A Future-Adaptable Password Scheme” (bcrypt). USENIX Annual Technical Conference, 1999. https://www.usenix.org/conference/1999-usenix-annual-technical-conference/future-adaptable-password-scheme
- Planck Collaboration. “Planck 2018 results. VI. Cosmological parameters”. Astronomy & Astrophysics 641, A6 (2020). https://arxiv.org/abs/1807.06209
- Shor, P. W. “Polynomial-Time Algorithms for Prime Factorization and Discrete Logarithms on a Quantum Computer”. SIAM Journal on Computing 26(5), 1997. https://arxiv.org/abs/quant-ph/9508027
- NIST. “NIST Releases First 3 Finalized Post-Quantum Encryption Standards” (August 13, 2024). https://www.nist.gov/news-events/news/2024/08/nist-releases-first-3-finalized-post-quantum-encryption-standards
- Chromium Blog. “Advancing Our Amazing Bet on Asymmetric Cryptography” (Chrome 124). https://blog.google/chromium/advancing-our-amazing-bet-on-asymmetric/
- Apple Security Research. “iMessage with PQ3: The new state of the art in quantum-secure messaging at scale” (2024). https://security.apple.com/blog/imessage-pq3/
- Kret and Schmidt. “The PQXDH Key Agreement Protocol”, Signal (rev. 3, 2023). https://signal.org/docs/specifications/pqxdh/
In Mexico, a “cyber” is a shop where you rent an internet-connected computer by the hour. Sometimes it was an internet café, but often it was the stationery shop on the corner, with a few computers at the back. ↩︎